
fieldeffect-mcp
MCP server for Field Effect (Covalence MDR — managed detection &response). Exposes the Field Effect MDR Portal REST API's organization,endpoint device, and Active Response reporting endpoints as MCP tools.
Naming note: MSPbots' own integration is registered as "Field Effect"(
subjectCode=FIELDEFFECT); the vendor's product name is "Covalence" /"Field Effect MDR". This MCP covers exactly the 4 GET endpoints MSPbotsitself has configured — see Known Gaps below for why the scope stopsthere.
MSPbots Connector
The MCP Gateway built for MSPs: visible, controlled, and your data stays where it belongs.
MSPbots Connector gives your AI clients one MCP URL to reach your entire MSP stack (RMM, PSA, documentation, security, finance), and gives you control over who can call which tool and a record of everything that was called.
Hosted service: connect.mspbots.ai · Free to use.
Why Connector
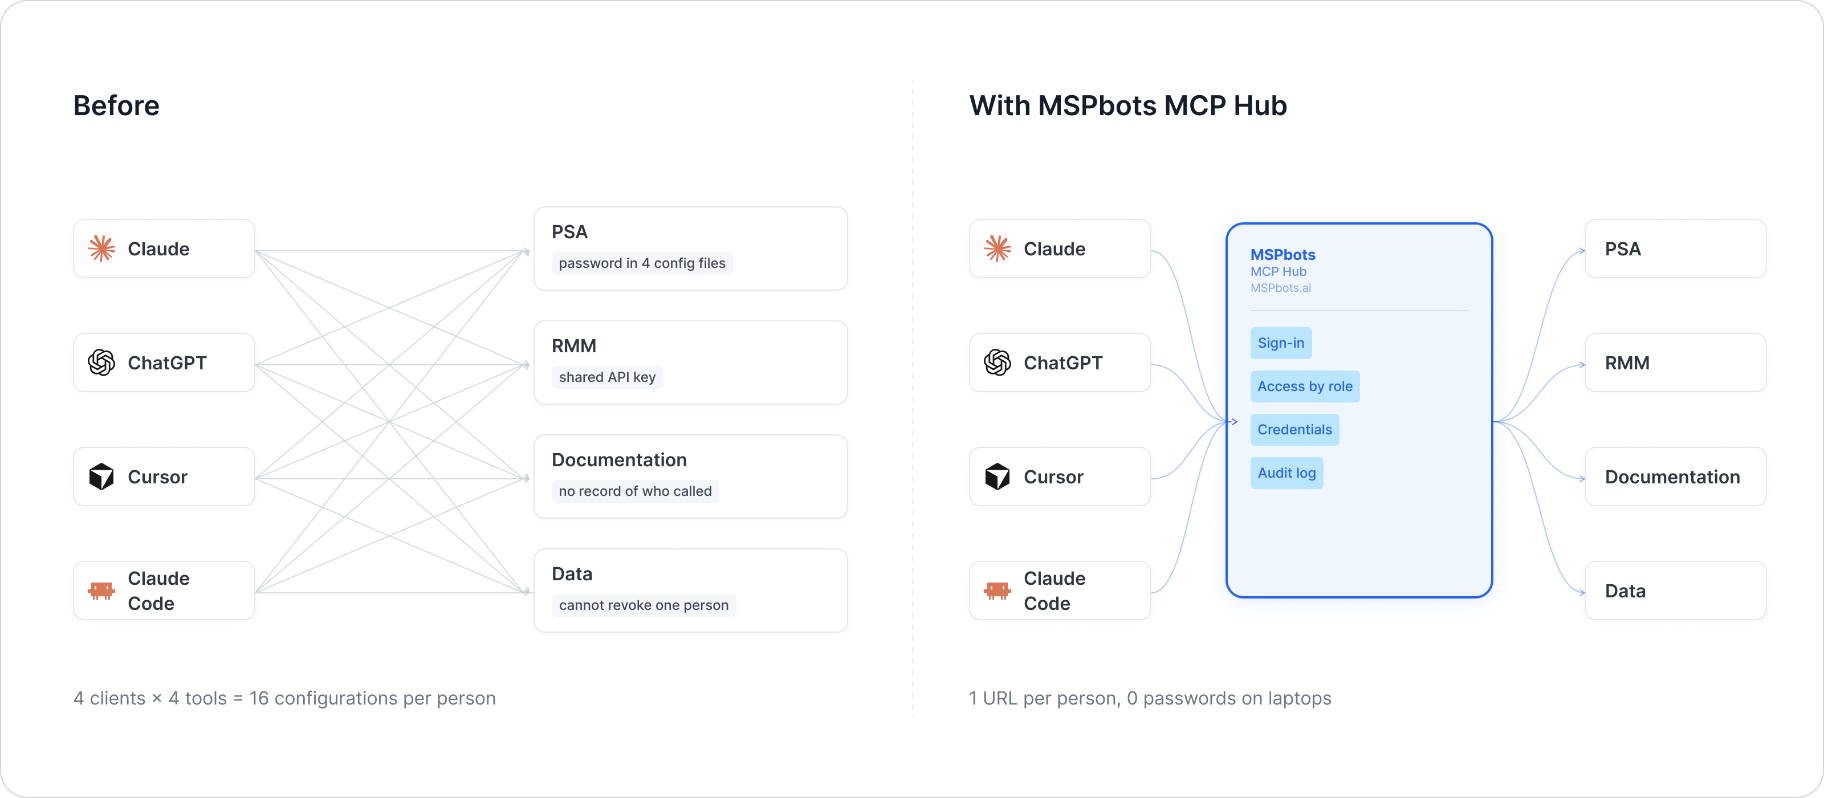
| Visible | Every tool call is logged: who, which vendor, when. Usage dashboard, CSV export, SIEM streaming. |
| Controlled | Role-based, per-tool allowlist. Deny by default. |
| Protected | Credentials encrypted per record. AI clients never see your vendor passwords or tokens. |
| MSP-native | Built for the MSP stack only: RMM, PSA, documentation, security, finance. |
Quick start
- Sign up at connect.mspbots.ai.
- Connect your vendors. Pick from 150+ connectors and authorize each one on the vendor's own page, or bring your own API keys. No extra vendor accounts needed.
- Set access. Create roles and decide which tools each role may call. Nothing is allowed until you allow it.
- Add your MCP URL to your AI client. Copy the URL from your Connector dashboard into Claude, ChatGPT, Cursor, VS Code, Gemini, Codex, or any MCP-capable client.
- Ask your AI to do real work, and watch every call appear in the audit log.
Features
Unified gateway
- One MCP URL for all your AI clients
- 150+ connectors across the MSP stack
- Custom MCP servers supported, free
- Authorization happens on each vendor's own page; the AI never sees passwords or tokens
- Bring your own credentials: use the vendor API keys you already have
- Multiple accounts per app; connect once, reuse across AI clients
- Tool search: finds the right action for the task
- One sign-in; vendor credentials are injected behind the scenes and OAuth tokens refresh automatically
Visibility
- Audit log for every tool call (who, which vendor, when)
- Usage dashboard: call volume, top vendors, error rate, per-user activity
- Export audit logs to CSV, or stream to Loki, Graylog, or LogScale (SIEM)
- Optional recording of tool arguments and result summaries (off by default, enabled per organization)
Control
- Per-role, per-tool allowlist, deny by default
- owner / admin / member roles
- SCIM provisioning with Entra ID, Okta, JumpCloud, and Google Workspace
Security
- Credentials encrypted one record at a time (AES-256-GCM, per-record key)
- AI clients authenticate with OAuth 2.1 + PKCE
- Vendor responses are scanned for prompt-injection patterns and returned as structured data. This is one layer of defense, not a guarantee against every attack.
- Static egress IP for customer firewall and API allowlisting
Pricing
Free.
Links: connect.mspbots.ai · mspbots.ai
Overview
- Stateless HTTP service. No credentials are ever persisted — each requestsupplies its own API key via a header, used only for the lifetime ofthat single request.
- Supports concurrent requests; per-request credential isolation is done viaPython
contextvars, not a global/shared client instance. - Entry points:
POST /mcp(MCP protocol) andGET /health(health check). - Default port:
8080(configurable viaMCP_HTTP_PORT).
Authentication
Field Effect authenticates with a static API key, created in the APIsection of the Field Effect MDR Portal. MSPbots' own integration conventionsends this key as an Authorization: Bearer <api-key> header, and thisserver forwards it exactly that way.
HEADER authentication parameters
| Header | Type | Required | Default | Allowed values | Description | Example |
|---|---|---|---|---|---|---|
X-FieldEffect-Api-Key |
string | Yes | None | None | Field Effect MDR Portal API Key, forwarded as the upstream Authorization: Bearer <key> request header |
a1b2c3d4e5f6... |
Missing the header returns 401:
{
  "error": "Missing credentials",
  "message": "This server requires the X-FieldEffect-Api-Key header",
  "required_headers": ["X-FieldEffect-Api-Key"],
  "optional_headers": []
}
Environment Variables
| Variable | Type | Required | Default | Description |
|---|---|---|---|---|
MCP_HTTP_PORT |
int | No | 8080 |
HTTP listen port |
MCP_HTTP_HOST |
string | No | 0.0.0.0 |
HTTP listen address |
FIELDEFFECT_BASE_URL |
string | No | https://services.fieldeffect.net/v1 |
Field Effect API base URL |
MCP Endpoint
POST /mcp— MCP protocol (streamable HTTP transport)GET /health— health check, returns{"status": "ok"}(pure local probe, does not depend on the Field Effect API)
Tool List
All 4 tools are plain GET calls, matching exactly how MSPbots itselfcalls this integration today. All are read-only (readOnlyHint=True).
| Tool | Function | Parameters |
|---|---|---|
fieldeffect_get_organizations |
List all organizations (customers) visible to this API Key | None |
fieldeffect_get_endpoint_devices |
List all endpoint devices (including risk level/score), paginated | page (optional), per_page (optional, default 50, hard limit 200, see Known Gaps) |
fieldeffect_get_endpoint_device_antivirus_details |
Get antivirus status details of the specified endpoint device | device_id (required) |
fieldeffect_get_active_response_actions |
List Active Response events (such as device isolation), paginated | page (optional), per_page (optional, default 50, hard limit 200, see Known Gaps) |
Tool return values are uniformly compact JSON strings (ensure_ascii=False, no indent); when a single response exceeds 20,000characters, the largest list field is automatically truncated and a truncated/original_count marker is attached. On error, a structurederror envelope {"error": {"code", "message", "retryable"}} is returned (code is taken from a fixed vocabulary:not_configured / unauthorized / not_found / invalid_argument / rate_limited /upstream_error); no exception is raised.
Test Example
# Health check
curl -s http://localhost:8080/health

# Call a tool via the MCP protocol (streamable HTTP) — requires an
# initialize handshake first per the MCP spec; abbreviated example below
# shows the tool-call request body only:
curl -s -X POST http://localhost:8080/mcp \
  -H "X-FieldEffect-Api-Key: <your-fieldeffect-api-key>" \
  -H "Content-Type: application/json" \
  -H "Accept: application/json, text/event-stream" \
  -H "mcp-session-id: <session-id-from-initialize>" \
  -d '{
    "jsonrpc": "2.0",
    "id": 1,
    "method": "tools/call",
    "params": {
      "name": "fieldeffect_get_organizations",
      "arguments": {}
    }
  }'
Live-verified (2026-07-29) against a real MDR Portal API key: all 4tools were called end-to-end through this running server —fieldeffect_get_organizations returned 41 real organizations,fieldeffect_get_endpoint_devices returned a paginated list (1719 devicestotal across 18 pages), fieldeffect_get_endpoint_device_antivirus_detailsreturned successfully (204, no AV data for that particular device — not anerror), and fieldeffect_get_active_response_actions returned 200.
API Reference
- Overview (public, no login required): https://support.fieldeffect.com/en/support/solutions/articles/16000206018-field-effect-apis-overview
- The full interactive Swagger/OpenAPI documentation is only accessiblefrom inside the MDR Portal's own Support section — it requires beinglogged into a Field Effect MDR Portal account, not just having an APIkey. No public Swagger/OpenAPI spec was found, and probing commonspec paths (
/swagger.json,/v1/openapi.json,/v1/api-docs, etc.)directly againstservices.fieldeffect.netall returned404.
Known Gaps
- Scope is exactly MSPbots' 4 configured endpoints, not the vendor'sfull API surface — same situation as
bvoip-mcp/contactscience-mcp/dropsuite-mcpearlier in this program: the vendor's fuller APIreference requires a portal login this session doesn't have, so therewas no larger accessible spec to weigh a broader scope against. page/per_pageparameters onget_endpoint_devicesandget_active_response_actionsare inferred, not confirmed — the vendordoesn't publish these endpoints' accepted query parameters anywhereaccessible. They were added because the live response shape({"items": [...], "page": 1, "per_page": 100, "total": ..., "pages": ..., "has_next": ..., "has_prev": ...}) strongly suggests a standardpage/per_page pagination scheme, but this has not been verified byactually passing those parameters and confirming a changed result.Because the vendor's own real per-page maximum is unconfirmed, thisserver does not defer to it and instead applies the Vendor MCP SOP's ownfallback ceiling:per_pagedefaults to 50 when omitted and is clampedto 200 server-side regardless of what's requested.- Response field shapes are whatever the live API returns — notindependently verified against a schema, since none is publiclyavailable.


