
dropsuite-mcp
MCP server for Dropsuite (NinjaOne SaaS Backup) — a cloud backupplatform for Microsoft 365 / Google Workspace data. Exposes its resellerREST API as MCP tools.
Naming note: MSPbots' own integration is registered as "Dropsuite"(
subjectCode=DROPSUITE); the vendor rebranded to "NinjaOne SaaS Backup"after being acquired by NinjaOne, but the API and credential fields areunchanged. This MCP covers exactly the 8 GET endpoints MSPbots itself hasconfigured — see Known Gaps below for why the scope stops there.
MSPbots Connector
The MCP Gateway built for MSPs: visible, controlled, and your data stays where it belongs.
MSPbots Connector gives your AI clients one MCP URL to reach your entire MSP stack (RMM, PSA, documentation, security, finance), and gives you control over who can call which tool and a record of everything that was called.
Hosted service: connect.mspbots.ai · Free to use.
Why Connector
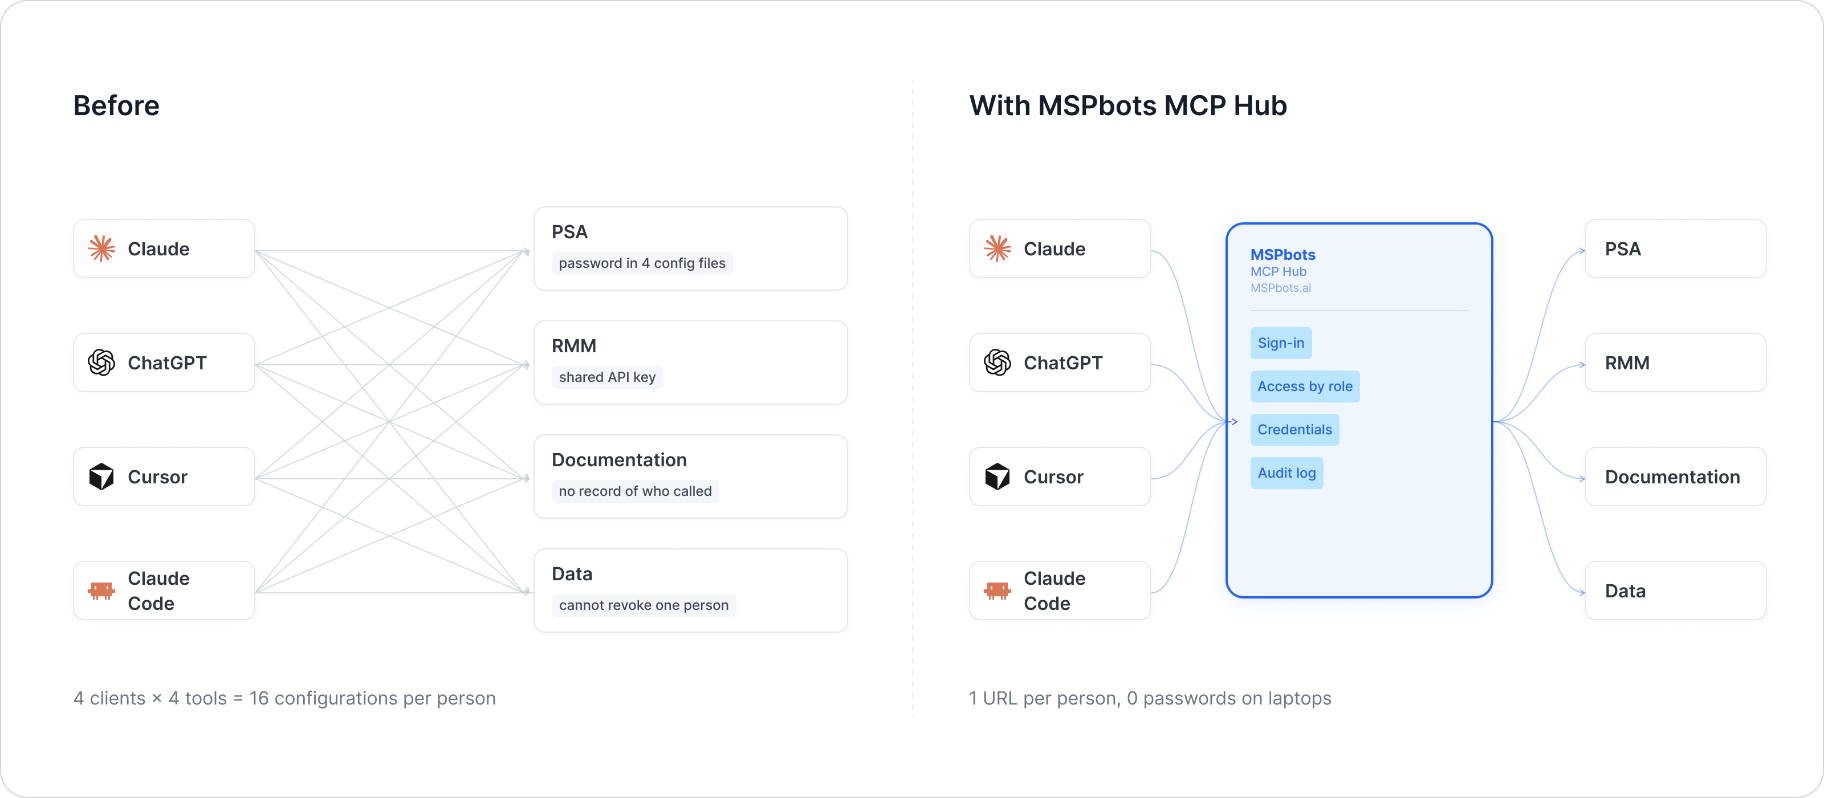
| Visible | Every tool call is logged: who, which vendor, when. Usage dashboard, CSV export, SIEM streaming. |
| Controlled | Role-based, per-tool allowlist. Deny by default. |
| Protected | Credentials encrypted per record. AI clients never see your vendor passwords or tokens. |
| MSP-native | Built for the MSP stack only: RMM, PSA, documentation, security, finance. |
Quick start
- Sign up at connect.mspbots.ai.
- Connect your vendors. Pick from 150+ connectors and authorize each one on the vendor's own page, or bring your own API keys. No extra vendor accounts needed.
- Set access. Create roles and decide which tools each role may call. Nothing is allowed until you allow it.
- Add your MCP URL to your AI client. Copy the URL from your Connector dashboard into Claude, ChatGPT, Cursor, VS Code, Gemini, Codex, or any MCP-capable client.
- Ask your AI to do real work, and watch every call appear in the audit log.
Features
Unified gateway
- One MCP URL for all your AI clients
- 150+ connectors across the MSP stack
- Custom MCP servers supported, free
- Authorization happens on each vendor's own page; the AI never sees passwords or tokens
- Bring your own credentials: use the vendor API keys you already have
- Multiple accounts per app; connect once, reuse across AI clients
- Tool search: finds the right action for the task
- One sign-in; vendor credentials are injected behind the scenes and OAuth tokens refresh automatically
Visibility
- Audit log for every tool call (who, which vendor, when)
- Usage dashboard: call volume, top vendors, error rate, per-user activity
- Export audit logs to CSV, or stream to Loki, Graylog, or LogScale (SIEM)
- Optional recording of tool arguments and result summaries (off by default, enabled per organization)
Control
- Per-role, per-tool allowlist, deny by default
- owner / admin / member roles
- SCIM provisioning with Entra ID, Okta, JumpCloud, and Google Workspace
Security
- Credentials encrypted one record at a time (AES-256-GCM, per-record key)
- AI clients authenticate with OAuth 2.1 + PKCE
- Vendor responses are scanned for prompt-injection patterns and returned as structured data. This is one layer of defense, not a guarantee against every attack.
- Static egress IP for customer firewall and API allowlisting
Pricing
Free.
Links: connect.mspbots.ai · mspbots.ai
Overview
- Stateless HTTP service. No credentials are ever persisted — each requestsupplies its own credentials via headers, used only for the lifetime ofthat single request.
- Supports concurrent requests; per-request credential isolation is done viaPython
contextvars, not a global/shared client instance. - Entry points:
POST /mcp(MCP protocol) andGET /health(health check). - Default port:
8080(configurable viaMCP_HTTP_PORT).
Authentication
Dropsuite authenticates with two static tokens (an Access Token and aReseller Token, both found on the "API Settings" page in the Dropsuite/NinjaOne SaaS Backup dashboard). Since every reseller/partner has its ownsite host, the base URL is also per-request rather than fixed.
Per the vendor's own documentation: "Sub-partners and resellers can useGET API calls to retrieve information about their organizations andusers" — write access is restricted to Direct Partners/Distributors, so areseller-scoped credential (like MSPbots' own) is inherently read-only.
HEADER authentication parameters
| Header | Type | Required | Default | Allowed values | Description | Example |
|---|---|---|---|---|---|---|
X-Dropsuite-Access-Token |
string | Yes | None | None | Dropsuite Authentication Token, forwarded as the upstream X-Access-Token request header |
a1b2c3d4-e5f6-7890-abcd-ef1234567890 |
X-Dropsuite-Reseller-Token |
string | Yes | None | None | Dropsuite Reseller Token, forwarded as the upstream X-Reseller-Token request header |
12345678-90ab-cdef-1234-567890abcdef |
X-Dropsuite-Site |
string | Yes | None | None | API host address of this reseller (each reseller has its own) | https://dropsuite.us |
Missing any of the three headers returns 401:
{
  "error": "Missing credentials",
  "message": "This server requires the X-Dropsuite-Access-Token, X-Dropsuite-Reseller-Token, and X-Dropsuite-Site headers",
  "required_headers": ["X-Dropsuite-Access-Token", "X-Dropsuite-Reseller-Token", "X-Dropsuite-Site"],
  "optional_headers": []
}
Environment Variables
| Variable | Type | Required | Default | Description |
|---|---|---|---|---|
MCP_HTTP_PORT |
int | No | 8080 |
HTTP listen port |
MCP_HTTP_HOST |
string | No | 0.0.0.0 |
HTTP listen address |
(No *_BASE_URL env var — the site host is per-reseller and alwayssupplied via the X-Dropsuite-Site header, never a fixed default.)
MCP Endpoint
POST /mcp— MCP protocol (streamable HTTP transport)GET /health— health check, returns{"status": "ok"}(pure local probe, does not depend on the upstream Dropsuite API)
Tool List
All 8 tools are plain GET calls with no required parameters — thismatches exactly how MSPbots itself calls this integration today. Each toolaccepts an optional extra_params pass-through dict for any additionalquery-string filters, since Dropsuite's full filter reference is onlyavailable through a partner-portal-gated PDF/Browsable API (seeKnown Gaps).
| Tool | Function | Parameters |
|---|---|---|
dropsuite_get_accounts |
List backup accounts (customers/organizations) under this reseller | extra_params: dict[str,str] | None |
dropsuite_get_users |
List backed-up mailboxes/users | extra_params: dict[str,str] | None |
dropsuite_get_contacts |
List backed-up contacts | extra_params: dict[str,str] | None |
dropsuite_get_calendars |
List backed-up calendars | extra_params: dict[str,str] | None |
dropsuite_get_tasks |
List backed-up tasks | extra_params: dict[str,str] | None |
dropsuite_get_onedrives |
List backed-up OneDrive accounts | extra_params: dict[str,str] | None |
dropsuite_get_sharepoints_domains |
List backed-up SharePoint domains | extra_params: dict[str,str] | None |
dropsuite_get_teams_and_groups_domains |
List backed-up Teams/Groups domains | extra_params: dict[str,str] | None |
Test Example
# Health check
curl -s http://localhost:8080/health

# Call a tool via the MCP protocol (streamable HTTP) — requires an
# initialize handshake first per the MCP spec; abbreviated example below
# shows the tool-call request body only:
curl -s -X POST http://localhost:8080/mcp \
  -H "X-Dropsuite-Access-Token: <your-access-token>" \
  -H "X-Dropsuite-Reseller-Token: <your-reseller-token>" \
  -H "X-Dropsuite-Site: https://dropsuite.us" \
  -H "Content-Type: application/json" \
  -H "Accept: application/json, text/event-stream" \
  -H "mcp-session-id: <session-id-from-initialize>" \
  -d '{
    "jsonrpc": "2.0",
    "id": 1,
    "method": "tools/call",
    "params": {
      "name": "dropsuite_get_accounts",
      "arguments": {}
    }
  }'
Live-verified (2026-07-29) against a real reseller test account: 6 ofthe 8 tools (get_accounts, get_users, get_contacts, get_calendars,get_tasks, get_onedrives) returned 200 with real data (an empty []list, since this test reseller currently has no linked accounts) calledthrough the actual running MCP server. See Known Gaps for the other 2.
API Reference
- Vendor overview: https://help.dropsuite.com/hc/en-us/articles/20422080552855-API-Settings
- The full method/parameter reference ("REST API - for subreseller ver1.00.pdf") is attached to a NinjaOne KB article(https://www.ninjaone.com/docs/backup/saas-backup/getting-started/rest-api-reference/)that redirects to a NinjaOne account login — not accessible without aportal login, only an API token. The vendor's own "Browsable API" (alive, self-documenting endpoint list) is likewise only reachable frominside an authenticated Dropsuite/NinjaOne SaaS Backup dashboard session.
Known Gaps
- Scope is exactly MSPbots' 8 configured endpoints, not the vendor's fullAPI surface — same situation as
bvoip-mcp/contactscience-mcpearlier in this program: the vendor's fuller API reference is gatedbehind a portal login this session doesn't have, so there was no largeraccessible spec to weigh a broader scope against. The vendor's own docsadditionally confirm resellers are restricted to GET calls only, so areseller credential (like MSPbots' own) couldn't reach write endpointseven if they were documented. dropsuite_get_sharepoints_domainsanddropsuite_get_teams_and_groups_domainsreturned a generic vendor-side500 {"errors":{"System":["Internal Server Error"]}}in live testingagainst the provided test account, while the other 6 endpoints returned200(with empty[]results, since the test reseller has no linkedaccounts). This looks like a vendor-side issue with enumeratingSharePoint/Teams domains when there's no linked data to return, ratherthan a request-format problem on this server's side — both tools areimplemented identically to the other 6 working ones. Not independentlyconfirmed against an account that actually has SharePoint/Teams-enabledbackups.


